One small agent finds malware, exposed backups, open ports and missing security patches — and blocks brute-force attackers. You see it all, and fix it, from one dashboard.
4 servers reporting
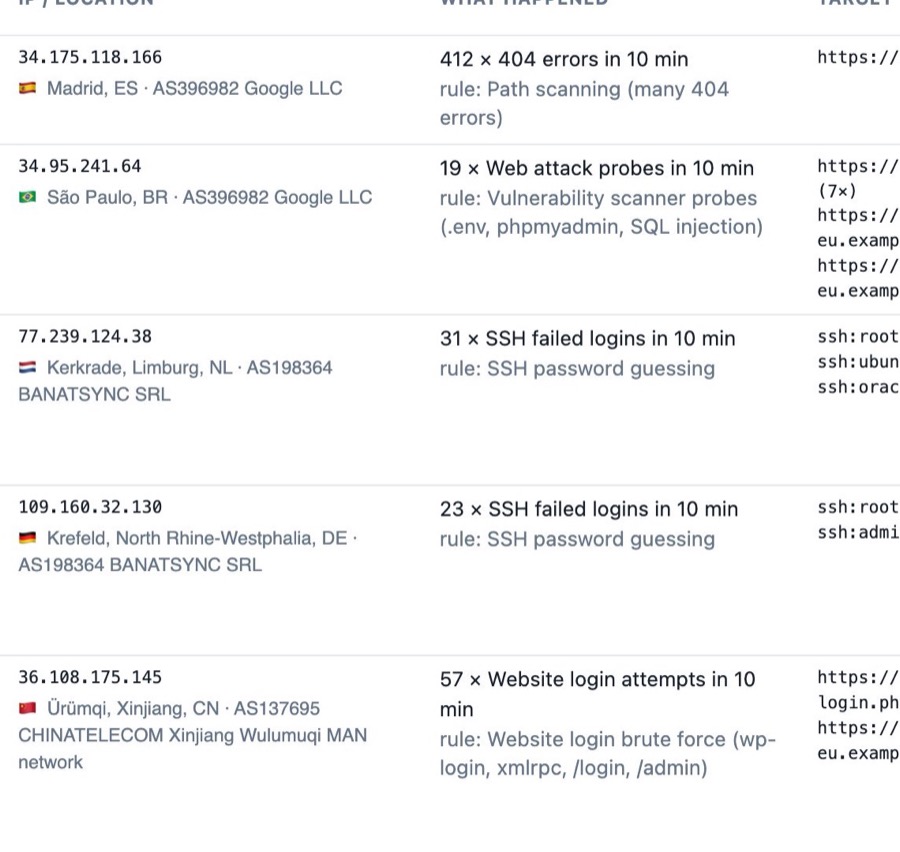
⛔ IP blocked by a rule


Most servers get hacked through something boring: an old PHP version, a forgotten backup.zip, a database port left open, or a password guessed after thousands of tries. AuditBash watches for all of it, all the time.
Patches without the busywork. It finds every language your server runs and installs their security updates every 2 hours — or alerts your team first.
Fix from the browser. Quarantine a webshell, delete a backup, block a port or an IP — one finding at a time or all critical ones at once.
Know who is attacking. See each attacker's country and city, and the exact login page or SSH account they tried.
Quick checks run every 2 hours. A deep scan of every website on the server runs daily, or whenever you click “Scan now”.
PHP, Python, Node.js, Ruby, Java, Go and more — security updates installed on schedule, with your sites checked before and after.
Every web root scanned for webshells, spam mailers, obfuscated PHP and crypto-miners. Quarantine or delete in one click.
.zip, .sql, .csv and .env files anyone can download — tested over HTTP exactly the way an attacker would.
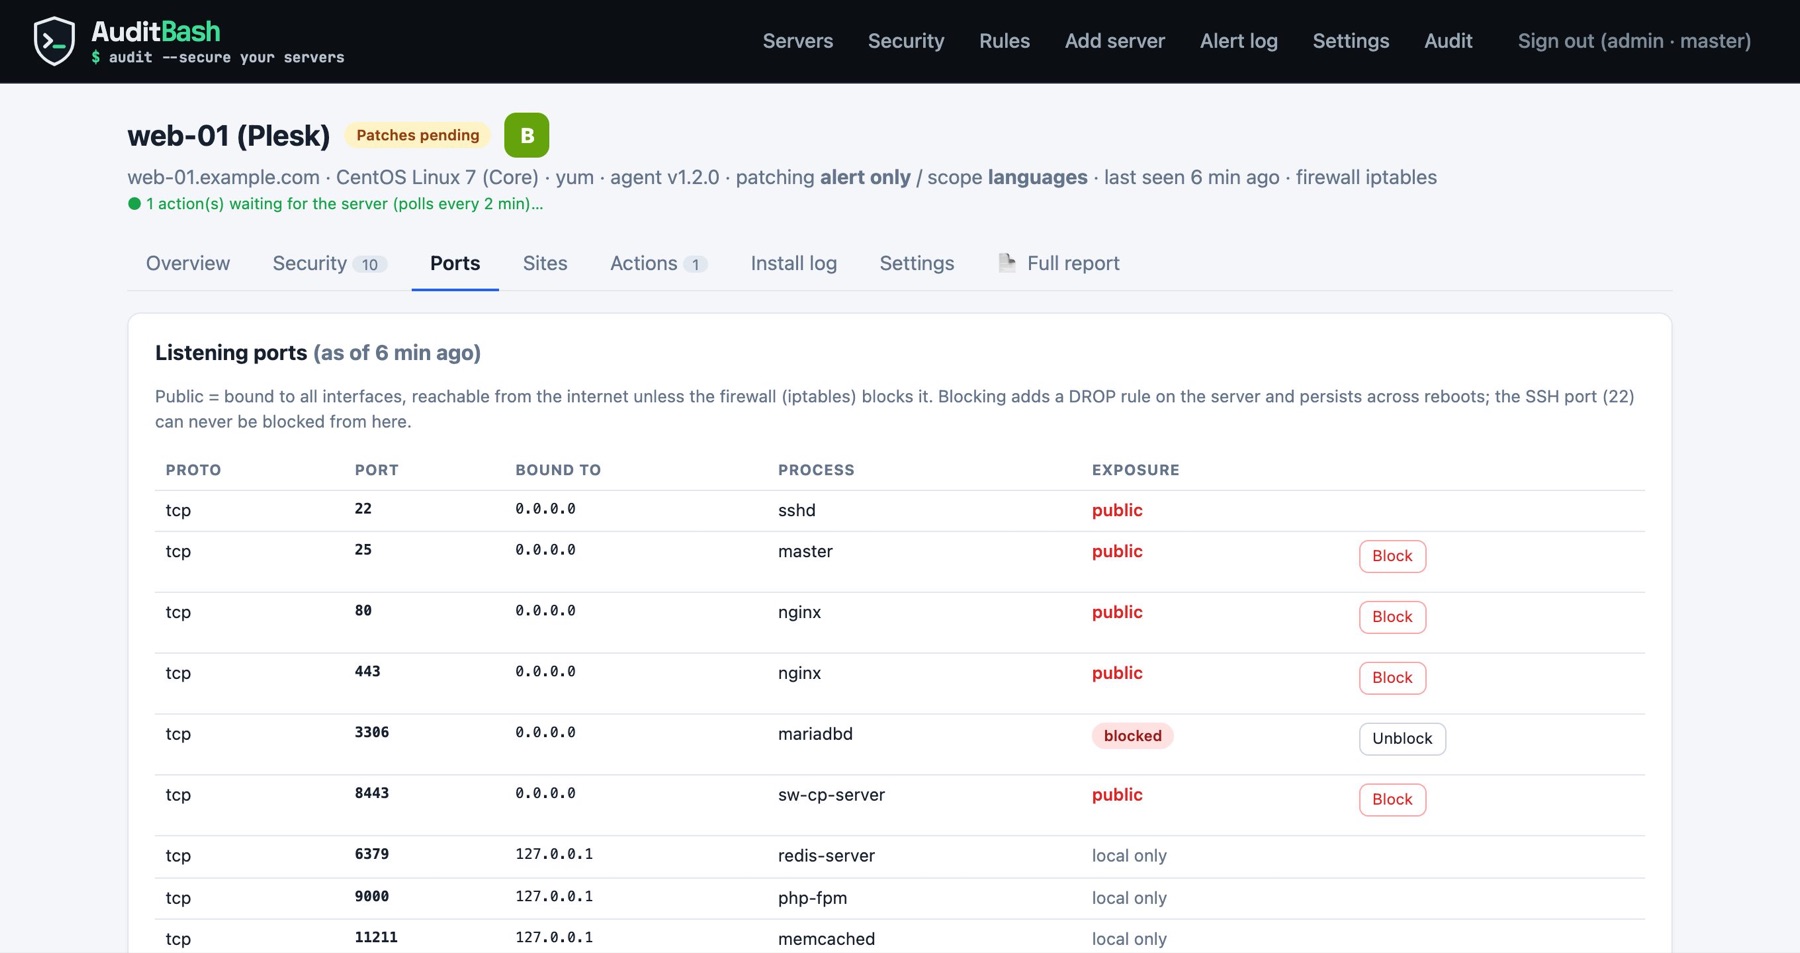
Every listening service listed, public databases flagged, and any port or IP blocked from the dashboard.
Rules like “10 failed SSH logins in 10 minutes → block for 24 hours”. Checked every 2 minutes, with the attacker's location.
Admin, operator and viewer roles, two-factor login, encrypted data at rest and a full audit log of every action.
No inbound ports, no agents to babysit. The server reports out to your dashboard and picks up your fixes.
Paste one command on the server. Watch each install step appear live in the dashboard.
curl … | sudo bashWithin minutes you get a security grade and every finding, ranked from critical to low.
auditbash scanPick findings — or select all critical — and choose quarantine, delete, block or patch.
Fix selectedEvery 2 hours it re-checks, patches, and emails you the moment something new turns up.
every 2 h
Select by severity, files or attacker IPs, then quarantine, delete or block in bulk.

Country, city and network of every blocked IP, plus the page or account they targeted.

Public databases and stray services flagged — blocked with one click, never your SSH port.
Every plan includes the full agent. You only choose where the dashboard lives.
$19 / month
Hosted by us. Install only the agent on your servers and start in minutes.
$99 / month
A dedicated dashboard installed on a server you own. Nothing is shared.
Prices in USD, billed monthly. Cancel any time. Compare plans →
Only if you tell it to. Each server is either “auto-apply security patches” or “alert only”. Fixes like blocking an IP or deleting a file run only when someone with the right role clicks them — or when a brute-force rule you switched on fires.
No. It connects out to the dashboard over HTTPS to send reports and pick up actions. Nothing new listens on your server.
No. It refuses to block the SSH port, the server's own IPs, private networks, anyone currently logged in over SSH, and any IP on your never-block list.
Ubuntu, Debian, RHEL, Rocky, AlmaLinux, Amazon Linux 2 and 2023, Fedora, Alpine and CentOS 7 — including servers run with Plesk or cPanel.
Your first audit takes one command and a few minutes. 14 days free on the Cloud Dashboard.